Understanding WireGuard VPN: How This Modern VPN Protocol Works
WireGuard is a lightweight, open-source VPN protocol that securely connects devices by encrypting their network traffic. Its streamlined design and modern cryptography support efficient performance without the complexity of many older VPN protocols. However, WireGuard alone does not guarantee privacy; your protection also depends on your VPN provider and how the connection is configured.
Whether you want to understand VPN technology, connect securely on public Wi-Fi, or access a private network remotely, understanding WireGuard can help you make a more informed decision. This guide explains how the protocol works, its main benefits and limitations, how it compares with OpenVPN and IPsec, and how to get started without unnecessary technical complexity.
What Is WireGuard VPN and How Does This VPN Protocol Work?
WireGuard is an open-source VPN protocol that establishes encrypted connections between configured peers. A peer can be a computer, phone, server, or another compatible device. Once the connection is established, the devices can exchange protected network traffic.
A virtual private network (VPN) creates a protected path through another network. The protocol defines how devices authenticate each other, establish encryption keys, and transfer data securely.
WireGuard is different from a complete VPN service. The protocol provides the underlying connection technology, while a VPN provider supplies infrastructure, server locations, applications, and other features needed for everyday use.
For example, you can install WireGuard on a Linux server and configure a client yourself. Alternatively, you can choose a commercial VPN service that uses WireGuard behind the scenes, so you do not have to manage servers or configuration files manually.
WireGuard was developed by Jason A. Donenfeld with a focus on simplicity, modern cryptography, and efficient operation. It is designed to be simple without relying on a long list of legacy cryptographic options.
WireGuard Security and Encryption
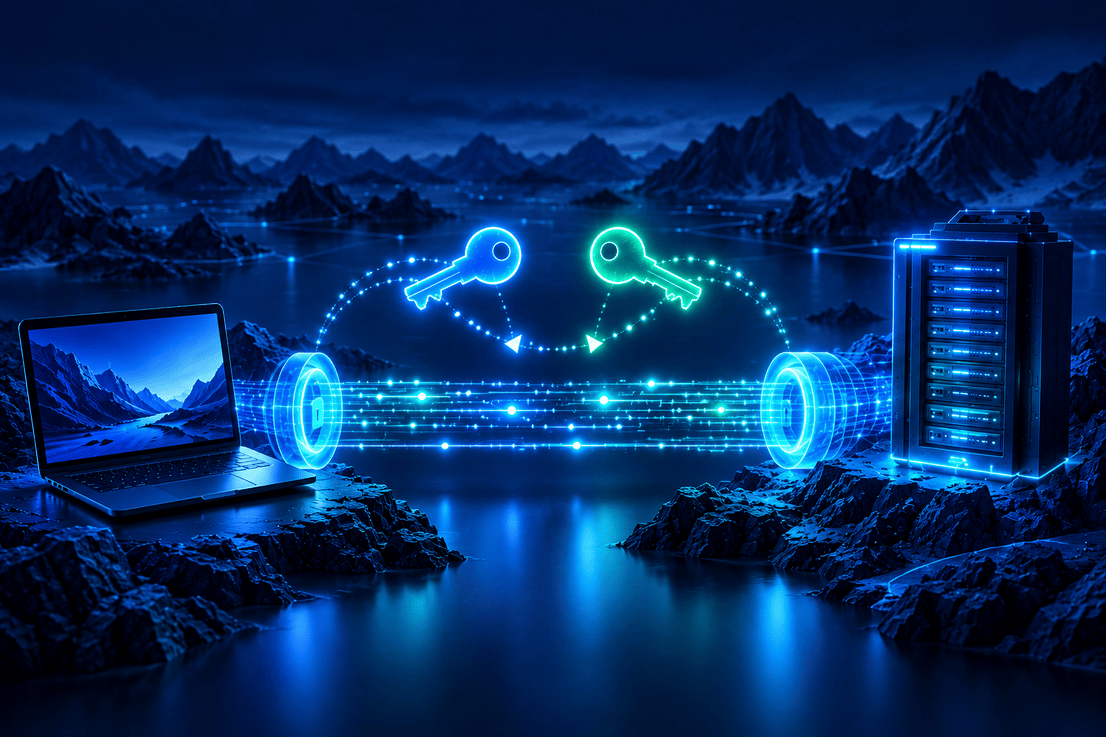
WireGuard creates an encrypted connection between configured peers using public and private keys, a cryptographic handshake, and authenticated encryption. After the peers establish shared session keys, they can exchange protected IP packets through the connection.
The process has several important stages.
1. Public Keys and Peer Authentication
Each WireGuard peer has a private key and a corresponding public key. The private key must remain secret, while the public key can be shared with the peers that need to communicate with that device.
This arrangement uses public key cryptography to establish trusted relationships between devices. Administrators configure which peers are permitted to communicate and which IP addresses each peer can send through the connection.
A public key is not a password, and sharing it does not reveal the corresponding private key. However, private keys must be protected because their compromise can weaken the security of the associated connection.
2. Key Exchange and the Cryptographic Handshake
Before transferring protected traffic, WireGuard performs a handshake based on the Noise Protocol Framework. This process authenticates the configured peers and establishes the cryptographic material required for secure communication.
The resulting session keys protect data packets. WireGuard periodically refreshes its session keys to support perfect forward secrecy, helping limit the impact of a later key compromise on previously captured traffic.
The handshake is designed to avoid unnecessary connection state for unauthenticated requests, which also helps mitigate certain denial-of-service risks.
3. Encryption and Secure Data Transfer
After the handshake, WireGuard encrypts and authenticates the packets sent through the connection. Its protocol specifies ChaCha20 for encryption and Poly1305 for authentication, combined as ChaCha20-Poly1305 authenticated encryption.
This means the receiving peer can check that protected data has not been modified in transit. Packets that fail the required authentication checks are rejected.
WireGuard uses UDP, or User Datagram Protocol, to carry its packets. UDP avoids the transport-level connection setup associated with TCP, although that does not guarantee faster speeds in every network.
4. Cryptokey Routing and Peer Configuration
WireGuard associates public keys with allowed IP addresses. This mechanism, known as cryptokey routing, helps determine which peer should receive outgoing packets and which source addresses are valid for incoming traffic.
For example, a remote-access configuration might permit a client to reach only a private home network. Another configuration could route all IPv4 internet traffic through a remote VPN server.
The actual result depends on the configured allowed IP ranges, operating-system routing rules, DNS settings, and any firewall rules.
What Are the Main Benefits and Drawbacks of WireGuard
The main benefits of the WireGuard VPN come from its focused design, modern cryptography, and efficient packet handling. These characteristics make it useful for personal connections, mobile devices, business networks, and commercial VPN applications.
Efficient Performance
WireGuard has a relatively compact implementation and a streamlined connection process. This can reduce processing overhead and help deliver faster speeds on suitable hardware and networks.
However, WireGuard is not automatically faster than every alternative. Server distance, network congestion, processor performance, routing, and packet loss can all affect the result. A well-configured OpenVPN service may perform better than a poorly configured WireGuard deployment.
A Compact Codebase
WireGuard was designed with a smaller codebase than many traditional VPN implementations. A compact codebase can make software easier to review, test, and maintain, potentially reducing the attack surface.
Code size alone does not prove security. Implementation quality, security research, maintenance, and configuration are also important.
Modern Cryptography
WireGuard uses a focused set of modern cryptographic algorithms rather than supporting a large collection of legacy options. Its cryptographic design includes Curve25519 for key exchange, ChaCha20-Poly1305 for authenticated encryption, BLAKE2s for hashing, SipHash24 for hash-table keys, and HKDF for key derivation.
These choices support a consistent security design and make the protocol easier to analyze than a system with many configurable cryptographic combinations.
Endpoint Roaming
WireGuard can adapt when a peer's network endpoint changes. For example, a mobile device may switch from Wi-Fi to a mobile network and acquire a different IP address.
The protocol can learn the peer's updated endpoint from authenticated traffic, allowing communication to continue without necessarily requiring a complete manual reconfiguration. Whether the transition feels seamless depends on the network, application, and configuration.
Potential Limitations of WireGuard
WireGuard's streamlined architecture does not include every feature found in a full VPN product. Some requirements need additional software or careful configuration, especially when operating a server yourself.
Limited built-in obfuscation: WireGuard does not aim to disguise VPN traffic by default. Networks that identify or restrict VPN traffic may block it. Additional tools can wrap or obscure the traffic, but they add complexity.
UDP-only transport: WireGuard sends packets over UDP rather than supporting native TCP tunnelling. This is suitable for many VPN use cases, but it can cause problems on networks that restrict UDP traffic.
Manual configuration: A self-hosted installation requires key management, peer definitions, IP addressing, routing, and firewall rules. Errors can prevent connections or expose resources unintentionally.
Privacy depends on the provider: The protocol does not define a provider's account system, data-retention policy, server selection, or logging practices. Those features must be assessed separately.
Post-quantum limitations: WireGuard does not provide post-quantum security by default. Its optional pre-shared-key mechanism can add another symmetric-key layer, but this should not be confused with a complete, standardized post-quantum migration.
These limitations do not make WireGuard inherently unsuitable. They mean that you should choose an implementation that fits your network, technical experience, and privacy requirements.
WireGuard VPN Protocol vs OpenVPN vs IPsec
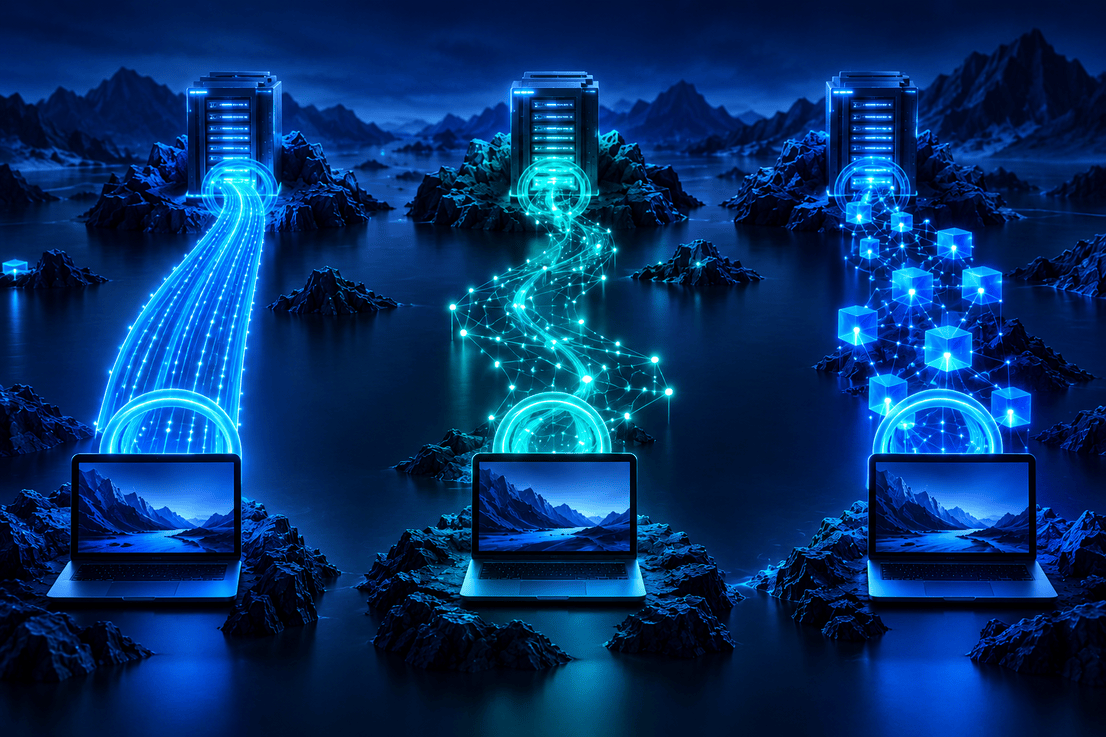
WireGuard, OpenVPN, and IPsec can all protect network traffic, but they differ in design, configuration, and transport options. The right choice depends on the network environment and the features you need.
Feature | WireGuard | OpenVPN | IPsec |
|---|---|---|---|
Design | Modern and streamlined | Flexible, with a broad feature set | A suite of protocols for IP-layer security |
Transport | UDP | UDP or TCP, depending on configuration | Commonly uses ESP, with NAT traversal options |
Cryptography | A focused, predefined set | Supports configurable cryptographic options | Depends on the IPsec protocols and negotiated algorithms |
Configuration | Relatively simple once peer settings are understood | Can involve more options and configuration choices | Varies by implementation and network environment |
Traffic obfuscation | Not built in | Depends on the setup and additional tools | Not a core guarantee of IPsec |
Common uses | Remote access, site-to-site links, VPN applications | Remote access and commercial VPN services | Enterprise networks, site-to-site VPNs, and remote access |
Which VPN Protocol Should You Choose?
WireGuard is a strong option when you want a streamlined protocol with modern cryptography and relatively straightforward peer configuration.
OpenVPN may suit environments that need flexible transport choices or compatibility with established deployments. Its ability to use TCP can be helpful on certain restrictive networks, although TCP tunnelling can introduce performance trade-offs.
IPsec is widely used in enterprise networking and can integrate with existing network infrastructure. Its configuration and capabilities vary depending on the implementation.
There is no universal winner. Compare the actual implementations and requirements rather than assuming that one protocol will always provide the best performance or security.
Is WireGuard a Secure VPN Protocol?
WireGuard is designed around modern cryptographic primitives and a carefully specified handshake. Its security benefits include authenticated encryption, peer authentication, replay protection, and forward secrecy for data traffic under the protocol's intended security assumptions.
Its security nevertheless depends on correct configuration, private-key protection, and the software implementation. A compromised device can expose data before it is encrypted or after it has been decrypted.
It is also important to distinguish encryption from anonymity. A VPN can hide your normal public IP address from websites when your traffic is routed through a remote server, but it does not prevent every form of tracking. Websites may still identify you through account logins, cookies, browser fingerprinting, or other information.
The VPN provider also becomes an important part of the trust relationship because it operates the remote endpoint through which your traffic passes.
Before choosing a provider, examine its privacy policy, security features, ownership, and data-handling practices. For example, Shieldway's no-logs policy explains which VPN activity it says it does not record and distinguishes that activity from the limited operational data needed to run the service.
WireGuard VPN Setup Guide
You can use WireGuard by configuring your own server or choosing a VPN provider that manages the infrastructure. Manual setup offers control, while a dedicated application is generally easier for people who do not want to manage networking details.
Option 1: Set Up a WireGuard Server on Linux
A basic self-hosted installation involves several steps:
Install WireGuard. Use your Linux distribution's package manager or follow the official installation and quick-start documentation.
Generate key pairs. Create private and public keys for the server and each client. Keep the private keys secure.
Configure the server. Define the interface address, private key, listening port, and authorized peers.
Configure the client. Add the server's public key, endpoint, client address, and allowed IP ranges.
Set up routing and firewall rules. Permit the required UDP traffic and configure forwarding if clients need to reach other networks or the internet through the server.
Start and test the connection. Confirm that the peers can communicate and that the routing rules behave as intended.
A configuration may contain entries such as Address, PrivateKey, PublicKey, AllowedIPs, and Endpoint. Their values depend on the network design, so do not copy an example into a live server without understanding what each setting does.
If you plan to set up a WireGuard server for remote access, make sure you also review DNS behaviour, firewall exposure, key rotation, software updates, and the access granted to each peer.
Option 2: Use WireGuard Through a VPN Application
If you do not want to create a server or maintain configuration files, a provider can manage the infrastructure and provide a client application. This can simplify server selection, connection management, and key handling.
Shieldway offers a managed WireGuard-based VPN application for Windows 10 and 11, macOS, and x86-64 Linux. You can find the current builds on the Shieldway download page.
This option can be easier for everyday use because you do not have to maintain your own server, configure peer relationships, or manage the underlying routing infrastructure. Check the provider's terms before connecting: Shieldway's free access currently requires enabling ByteConnect bandwidth sharing, and disabling that feature also disconnects the VPN.
WireGuard itself is open-source software, but that does not mean every commercial VPN service that uses it is free. The protocol, the application, and the service are separate things.
WireGuard and the Future of VPN Technology
WireGuard has helped popularize a modern approach to VPN design: a focused protocol, a limited set of cryptographic choices, and a simpler model for creating encrypted connections. Its availability across multiple operating systems also makes it useful for both personal and professional networking.
However, the future of VPN technology will depend on more than protocol design. Secure implementations, transparent privacy practices, strong device security, and careful key management will remain essential.
For users, the most practical choice is to select a solution that balances security, compatibility, usability, and trust. A protocol can provide a strong technical foundation, but the overall VPN experience also depends on the application and the service operating the servers.
Frequently Asked Questions
These answers address common questions about WireGuard's security, compatibility, cost, and practical use.
1. What is WireGuard, and how does it work?
WireGuard is an open-source VPN protocol that creates encrypted connections between configured peers. It uses public-key authentication and a cryptographic handshake to establish session keys, then protects data packets sent between the peers.
2. Is WireGuard secure?
WireGuard uses modern cryptography and authenticated encryption, making it a strong option when correctly implemented and configured. Security also depends on device protection, private-key handling, software maintenance, and the VPN provider's practices.
3. What encryption does WireGuard use?
The protocol specifies ChaCha20-Poly1305 for authenticated encryption and Curve25519 for key exchange. It also uses BLAKE2s for hashing, SipHash24 for hash-table keys, and HKDF for key derivation.
4. Is WireGuard better than OpenVPN?
Neither protocol is always better. WireGuard has a streamlined design and a focused cryptographic suite, while OpenVPN offers flexible configuration and supports both UDP and TCP transports. The best option depends on your network and requirements.
5. How does WireGuard compare with IPsec?
WireGuard is a focused VPN protocol with a relatively simple configuration model. IPsec is a suite of protocols used to secure IP communications and is common in enterprise networks. Both can provide strong protection when correctly implemented.
6. Is WireGuard free to use?
The WireGuard software is open source and available without a protocol licensing fee. However, running a server may involve hosting and maintenance costs, while commercial VPN providers may charge for their services. Free access from a provider may also come with conditions or limitations.
7. Does WireGuard hide your IP address?
When your traffic is routed through a remote VPN endpoint, websites generally see the endpoint's public IP address rather than your usual public address. This does not make you completely anonymous or prevent tracking through accounts, cookies, or browser fingerprinting.
8. Does WireGuard Work With UDP, NAT, and Firewalls?
WireGuard uses UDP to transport its packets. It does not natively tunnel directly over TCP, although separate tools can wrap its traffic in another transport when necessary.
9. Which operating systems support WireGuard?
WireGuard implementations are available for Linux, Windows, macOS, Android, and iOS. However, a specific VPN application's supported platforms may differ, so check the provider's current compatibility information before installing it.
10. How do you set up a WireGuard VPN?
You can install WireGuard on compatible devices, generate key pairs, configure peers, define allowed IP addresses, and set up routing and firewall rules. Alternatively, a VPN application can manage much of this process for you.
11. What is the difference between WireGuard and a VPN provider?
WireGuard is the protocol that establishes and protects the connection. A VPN provider operates servers and may supply applications, account management, server locations, and additional privacy or security features.
12. Can you use WireGuard without running your own server?
Yes. A VPN provider can operate the servers and supply an application or configuration for connecting. Running your own server is optional, not a requirement of the protocol.
Conclusion: Is WireGuard Worth Using?
WireGuard is a modern VPN protocol built on state-of-the-art cryptography, secure encryption keys, and a streamlined design. The WireGuard VPN protocol creates a secure VPN tunnel, supports online privacy, and offers strong security with fewer lines of code. Its development and use within the Linux kernel have helped make it a modern cryptographic option for users seeking a secure protocol.
Choosing the right type of VPN depends on your needs. Protocols like OpenVPN remain useful alternatives, so compare WireGuard with OpenVPN or IPsec before deciding. WireGuard can offer faster speeds in some environments, but packet loss, server distance, and network quality affect performance. Its ease of use can make it easier to use across supported systems, including a mobile device running macOS alternatives or iOS-compatible WireGuard software.
A Simpler Way to Use WireGuard
If you want an easy-to-use VPN without managing configuration files or encryption keys yourself, Shieldway offers a practical option. It can simplify your VPN connection without requiring you to set up a WireGuard server manually. This commercial VPN service is designed to make WireGuard more accessible, while its free VPN access requires enabling ByteConnect bandwidth sharing.
WireGuard is an open-source VPN protocol, but that does not mean all VPN services are free. Whether you choose a free VPN or commercial VPN, review the provider's privacy terms and security practices to protect your online privacy. For users who value a simple setup guide and a straightforward VPN experience, Shieldway may be easier to use than manual configuration.